
Third-Party Risk Is a Board Issue Now, Not a Procurement Checklist
Insight . Intelligence . Accountability
A new wave of professionals is transforming Governance, Risk, and Compliance from a rigid framework into a dynamic force for trust, innovation, and resilience. Governance, Risk, and Compliance (GRC) has long been associated with boardrooms and bureaucracy—a domain reserved for executives and auditors. But that image is changing fast.
Third-Party Risk Is a Board Issue Now, Not a Procurement Checklist
Dr Foluso Amusa, PhD — Founder & President, IGRCFP
3 August 2026
Outsourcing does not outsource accountability. Regulators have said this for years. Boards are only now starting to act as though they believe it.
Most institutions can produce a vendor risk register on request. Far fewer can answer, with confidence, a harder question: if our single largest third-party provider — the one processing KYC checks, or hosting core banking infrastructure, or running customer due diligence screening — suffered a serious operational failure tomorrow, what would happen to our customers, our regulatory obligations, and our board's ability to explain what happened? That question exposes the gap between third-party risk management as a procurement discipline and third-party risk management as a governance discipline, and it is the second version that regulators now expect.
The regulatory logic here is not new, but it has hardened. Across banking, insurance and increasingly non-financial regulated sectors, supervisors have made clear that an institution cannot outsource its accountability along with the activity itself. A failure at a critical outsourced provider is, from the regulator's perspective, a failure of the institution's own control environment — full stop. That framing puts third-party risk squarely inside the board's risk appetite conversation, alongside credit risk, market risk and financial crime risk, rather than treating it as a category owned three or four levels down the organisation.
The Extended Enterprise Has Outgrown Its Governance Model
The practical difficulty is that the modern institution's dependency web has grown faster than most governance frameworks have adapted. Core infrastructure increasingly sits with a small number of cloud providers, creating concentration risk that no single institution can diversify away on its own. KYC, screening and monitoring functions are routinely outsourced or augmented by third-party data and technology providers. Even governance functions themselves — internal audit co-sourcing, external MLRO support, compliance monitoring — now regularly involve external parties operating inside the institution's control environment. Each relationship is individually reasonable. Collectively, they represent a risk surface that a procurement-led due diligence process, run once at onboarding and revisited annually if at all, was never designed to manage.
A vendor risk register that gets updated once a year is not third-party risk management. It's an audit artefact.
Four Things That Separate Real Third-Party Governance from a Checklist
Effective third-party risk management rests on a small number of disciplines, consistently applied rather than periodically performed. First, due diligence at onboarding needs to be proportionate to criticality — a marketing vendor and a core banking processor should never go through the same template. Second, monitoring needs to be continuous rather than annual, with defined triggers — a security incident, a regulatory action, a change of ownership — that force an off-cycle reassessment. Third, contracts need genuine step-in and exit rights, tested in principle before they are needed in practice, not discovered to be inadequate during an actual failure. And fourth, and most often missing, critical third-party concentration needs to be reported to the board directly, in terms the board can act on — not buried in an operational risk appendix that gets nodded through.
None of this requires exotic tooling. It requires a board that treats its extended enterprise as part of its own control environment, because that is precisely how regulators, customers and — eventually — courts will treat it too.
This article reflects the author's professional view and is intended for general awareness. It does not constitute regulatory or legal advice.
Your email address will not be published. Required fields are marked with *
CPMI and IOSCO Release New Guidance on Managing Business Risks in Financial Market Infrastructures
The Committee on Payments and Market Infrastructures (CPMI) and IOSCO have released final guidance to help financial market infrastructures strengthen their approach to managing business risks and preparing for potential financial losses. The guidance clarifies existing requirements under Principle 15 of the Principles for Financial Market Infrastructures, following an assessment that identified weaknesses in how some institutions were applying the standards.
# Telemedicine CEO Sentenced to 19 Years Over $1 Billion Medicare Fraud Scheme
A Kansas healthcare technology executive has been sentenced to 19 years in prison for his role in a fraud scheme that generated more than $1 billion in claims against Medicare and other federal healthcare programmes. The case exposed how fraudulent medical orders, illegal kickbacks and deceptive telemedicine practices were used to exploit public healthcare funds.
FATF Warns Gaming and Gambling Sectors Face Growing Financial Crime Risks
The Financial Action Task Force (FATF) has identified new ways criminals are exploiting gaming and gambling platforms to move money, evade controls and support wider criminal activity. With online and cross-border gambling expanding rapidly, the FATF has issued new risk indicators to help regulators, financial institutions and industry operators detect suspicious activity and respond to money laundering, terrorist financing and other financial crime risks.
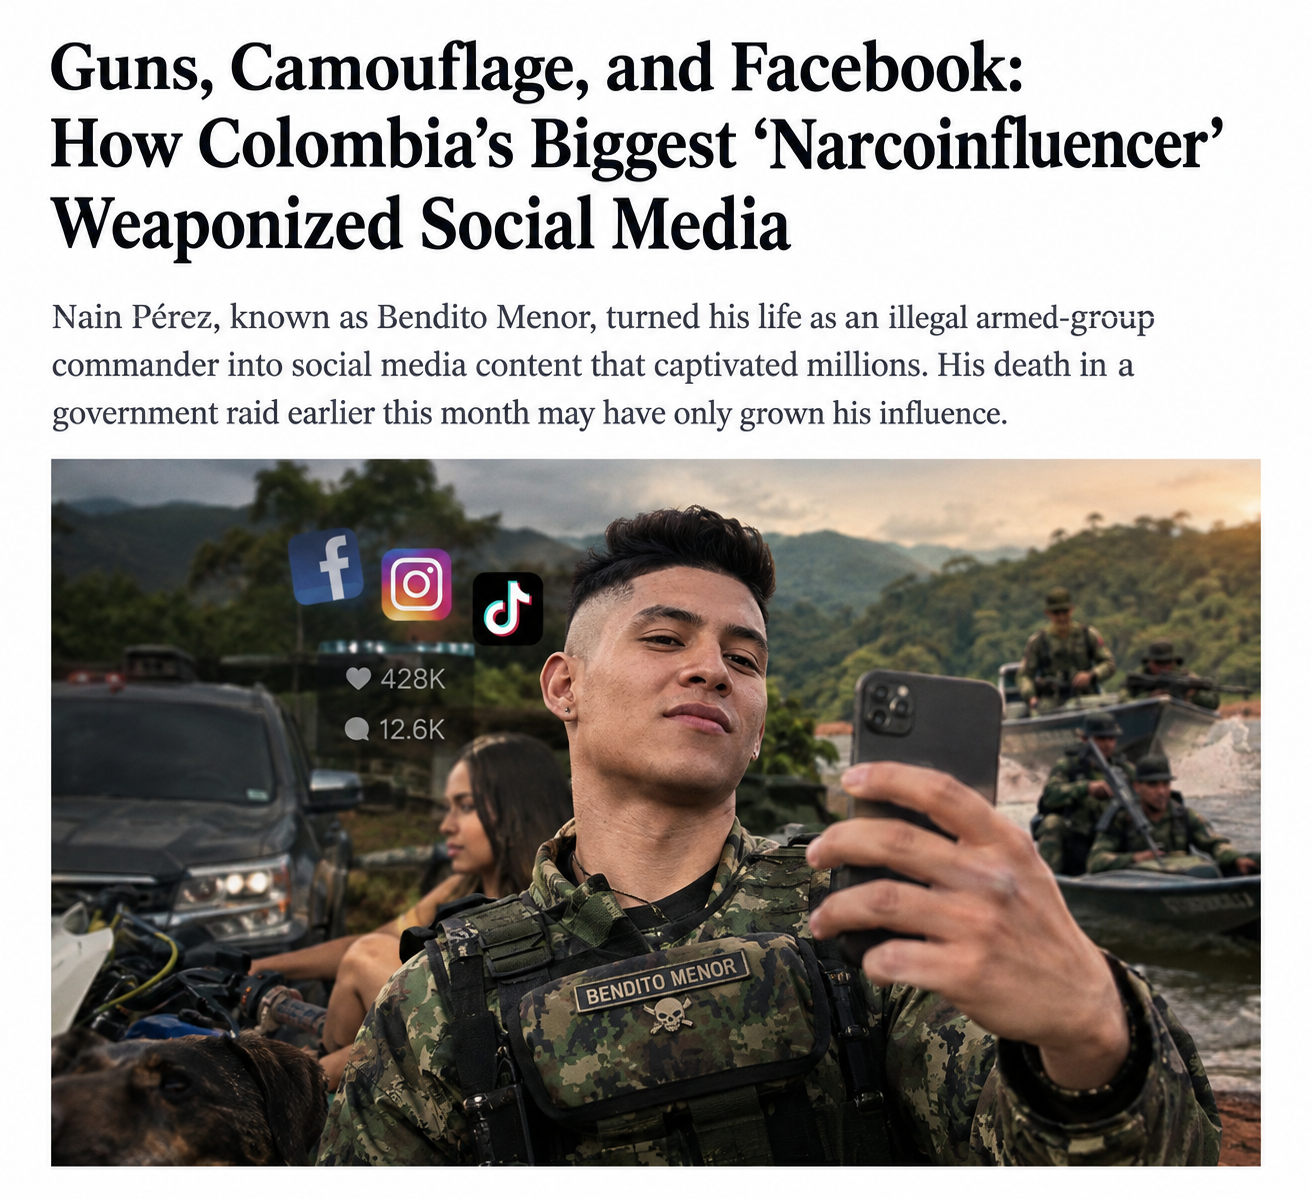
Guns, Camouflage and Facebook: How Colombia’s ‘Narcoinfluencer’ Turned Crime Into Content
Nain Pérez, known online as Bendito Menor, built a huge following by mixing images of money, romance and armed life with a criminal persona. His rise shows how social media can turn organized crime into something dangerously close to celebrity culture.
ENISA Warns Digital Dependencies Are Expanding Europe’s Cyber Attack Surface
Europe’s growing reliance on interconnected digital technologies is creating new cybersecurity challenges, with ENISA warning that increasing digital dependencies could widen the region’s exposure to cyber threats, vulnerabilities and potential disruptions across critical sectors.
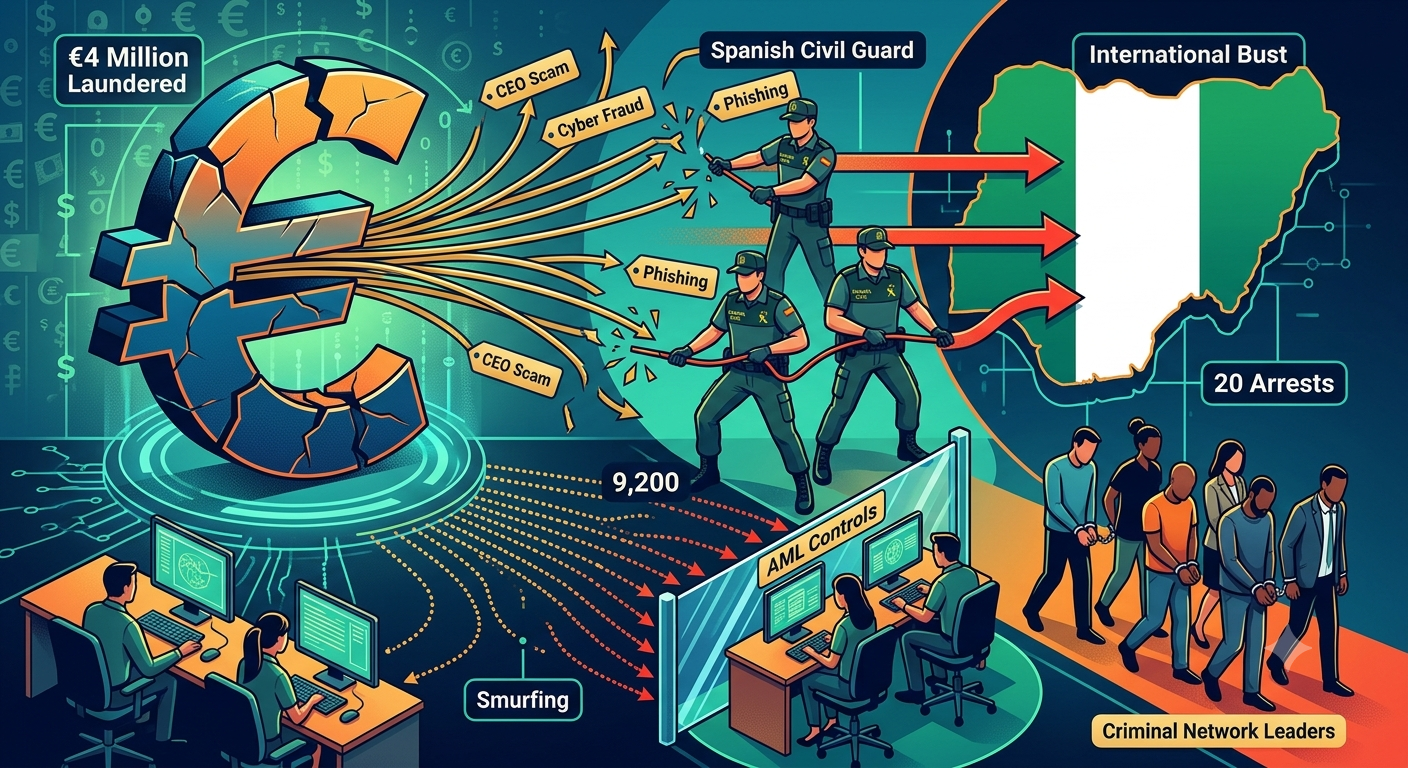
A network that laundered more than four million euros from scams by sending the money to Nigeria falls
Spanish Police Bust €4 Million International Money Laundering Ring Bound for Nigeria. The Spanish Civil Guard has dismantled a criminal network responsible for laundering over €4 million generated through cyber fraud, CEO scams, and identity theft across Europe. The organization utilized "smurfing"—splitting large illicit funds into more than 9,200 small-wire transfers using falsified passports and stolen identities—to bypass anti-money laundering controls and funnel cash into Nigeria. The two-phase operation led to 20 arrests, investigations into 11 others, and raids targeting key leaders in Bilbao as well as several complicit money transfer agencies.
No recommended articles found.