
The Fraud–AML Wall Is Coming Down. Is Your Function Ready?
Insight . Intelligence . Accountability
A new wave of professionals is transforming Governance, Risk, and Compliance from a rigid framework into a dynamic force for trust, innovation, and resilience. Governance, Risk, and Compliance (GRC) has long been associated with boardrooms and bureaucracy—a domain reserved for executives and auditors. But that image is changing fast.
The Fraud–AML Wall Is Coming Down. Is Your Function Ready?
Dr Foluso Amusa, PhD — Founder & President, IGRCFP
3 August 2026
For twenty years, fraud teams and AML teams have sat in different parts of the org chart, run different systems, and answered to different KPIs. The criminals stopped respecting that boundary a long time ago.
Walk into most mid-sized financial institutions and you will still find two functions that, on paper, exist to catch the same money: a fraud team focused on preventing loss at the point of transaction, and an anti-money laundering team focused on detecting and reporting suspicious activity after the fact. They typically run different case management systems, report through different lines, and are measured against different objectives — fraud loss ratios on one side, suspicious activity report quality and timeliness on the other. That structural separation made a certain amount of sense when the typologies themselves were separate: card fraud was a fraud problem, layering was a money laundering problem, and the two rarely met.
That separation no longer reflects how financial crime actually happens. Authorised push payment fraud is the clearest example: a victim is deceived into authorising a transfer, the funds land in a mule account opened using synthetic or stolen identity, and the proceeds are layered through a chain of onward transfers before the fraud is even reported. The initial event is a fraud. Everything that happens next is money laundering. A function that only looks at one half of that chain will always be a step behind, because the intelligence that would let it get ahead — the mule account patterns, the beneficiary network, the velocity signals — sits on the other side of an internal wall that the criminal network doesn't know exists.
Why Convergence Is Now a Regulatory Expectation, Not Just a Best Practice
Regulators have started to say the quiet part out loud. Supervisory commentary in multiple jurisdictions now explicitly references the expectation that institutions understand the connections between fraud and money laundering typologies, rather than treating them as unrelated risk categories with unrelated controls. That shift matters for governance as much as for detection: a board that receives separate, uncorrelated fraud and AML risk reports is not seeing the actual risk picture, and an institution that cannot demonstrate a joined-up view of financial crime risk is increasingly exposed on both the regulatory and the reputational front.
A unified financial crime function isn't a reorganisation exercise. It's a data and intelligence exercise that happens to require some reorganisation.
What a Converged Function Actually Looks Like
The institutions making real progress here are not necessarily the ones who have merged fraud and AML into a single reporting line overnight — organisational change of that scale carries its own risk and rarely survives contact with entrenched systems and skill sets. The more durable pattern is a converged intelligence layer sitting above both functions: shared entity resolution, so a customer or counterparty flagged in one system is visible in the other; cross-trained analysts who understand both typologies well enough to recognise when a fraud case is actually the front end of a laundering chain; and unified case management that lets an investigation move seamlessly from loss prevention to suspicious activity reporting without starting from zero.
None of that requires a wholesale technology replacement. It requires a deliberate decision, usually made at MLRO or Chief Risk Officer level, that fraud and financial crime intelligence will be treated as one data estate even where the teams consuming it remain organisationally distinct. Institutions that make that decision now, ahead of the point where a regulator or a loss event forces the issue, will find the transition considerably less painful than those who wait.
This article reflects the author's professional view and is intended for general awareness. It does not constitute regulatory or legal advice.
Your email address will not be published. Required fields are marked with *
CPMI and IOSCO Release New Guidance on Managing Business Risks in Financial Market Infrastructures
The Committee on Payments and Market Infrastructures (CPMI) and IOSCO have released final guidance to help financial market infrastructures strengthen their approach to managing business risks and preparing for potential financial losses. The guidance clarifies existing requirements under Principle 15 of the Principles for Financial Market Infrastructures, following an assessment that identified weaknesses in how some institutions were applying the standards.
# Telemedicine CEO Sentenced to 19 Years Over $1 Billion Medicare Fraud Scheme
A Kansas healthcare technology executive has been sentenced to 19 years in prison for his role in a fraud scheme that generated more than $1 billion in claims against Medicare and other federal healthcare programmes. The case exposed how fraudulent medical orders, illegal kickbacks and deceptive telemedicine practices were used to exploit public healthcare funds.
FATF Warns Gaming and Gambling Sectors Face Growing Financial Crime Risks
The Financial Action Task Force (FATF) has identified new ways criminals are exploiting gaming and gambling platforms to move money, evade controls and support wider criminal activity. With online and cross-border gambling expanding rapidly, the FATF has issued new risk indicators to help regulators, financial institutions and industry operators detect suspicious activity and respond to money laundering, terrorist financing and other financial crime risks.
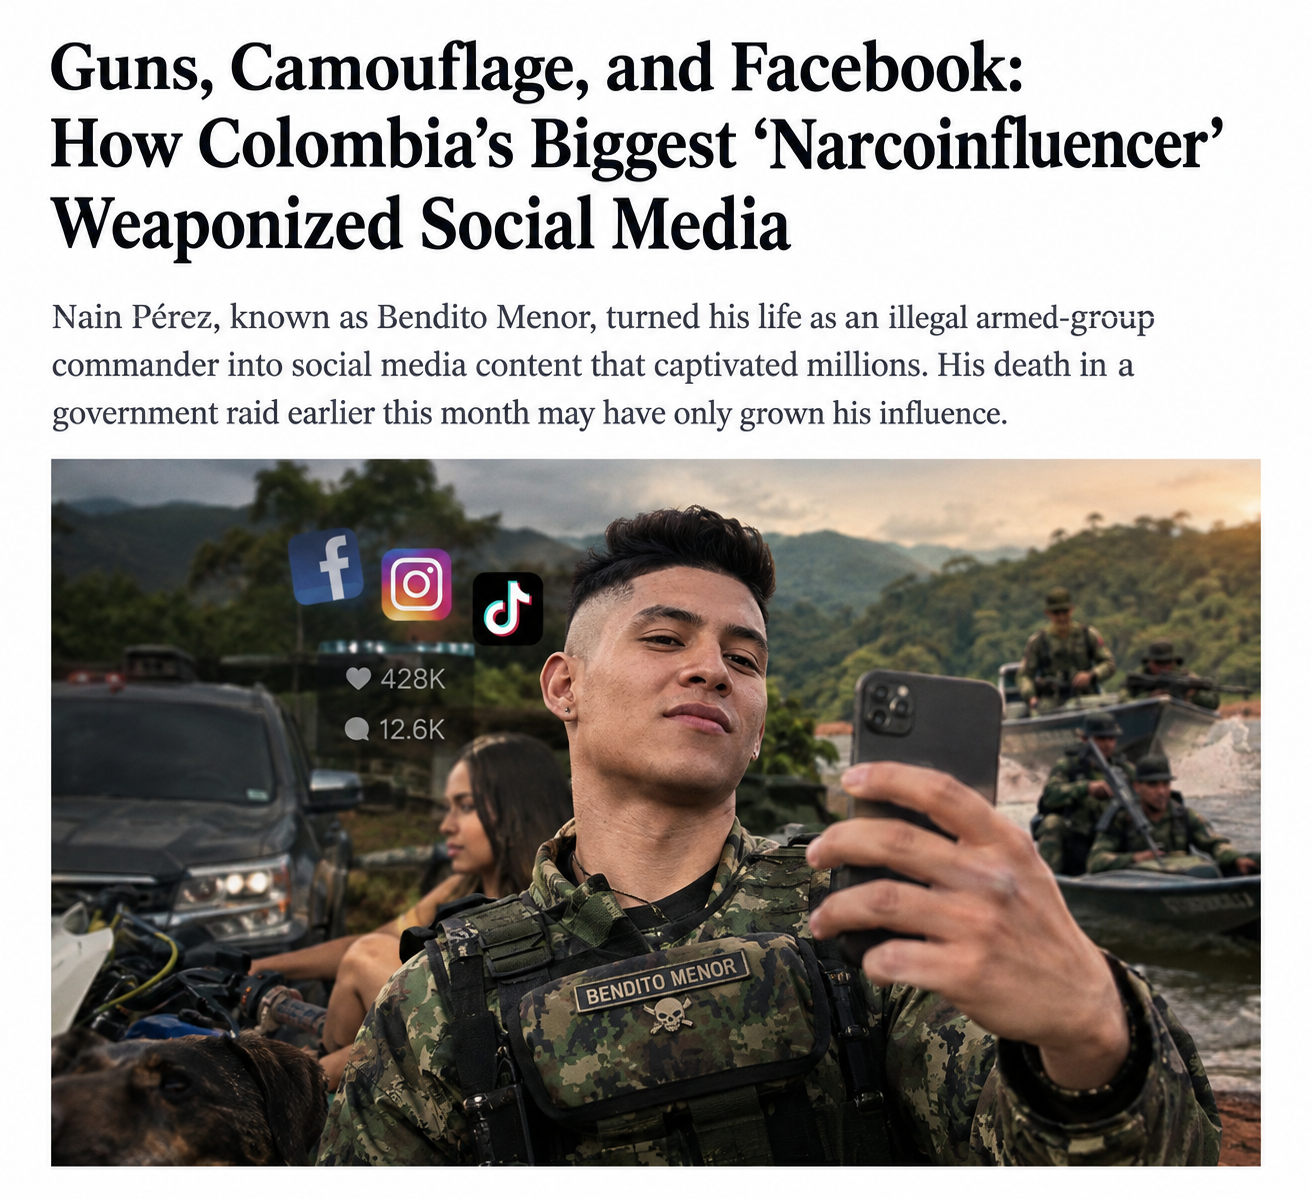
Guns, Camouflage and Facebook: How Colombia’s ‘Narcoinfluencer’ Turned Crime Into Content
Nain Pérez, known online as Bendito Menor, built a huge following by mixing images of money, romance and armed life with a criminal persona. His rise shows how social media can turn organized crime into something dangerously close to celebrity culture.
ENISA Warns Digital Dependencies Are Expanding Europe’s Cyber Attack Surface
Europe’s growing reliance on interconnected digital technologies is creating new cybersecurity challenges, with ENISA warning that increasing digital dependencies could widen the region’s exposure to cyber threats, vulnerabilities and potential disruptions across critical sectors.
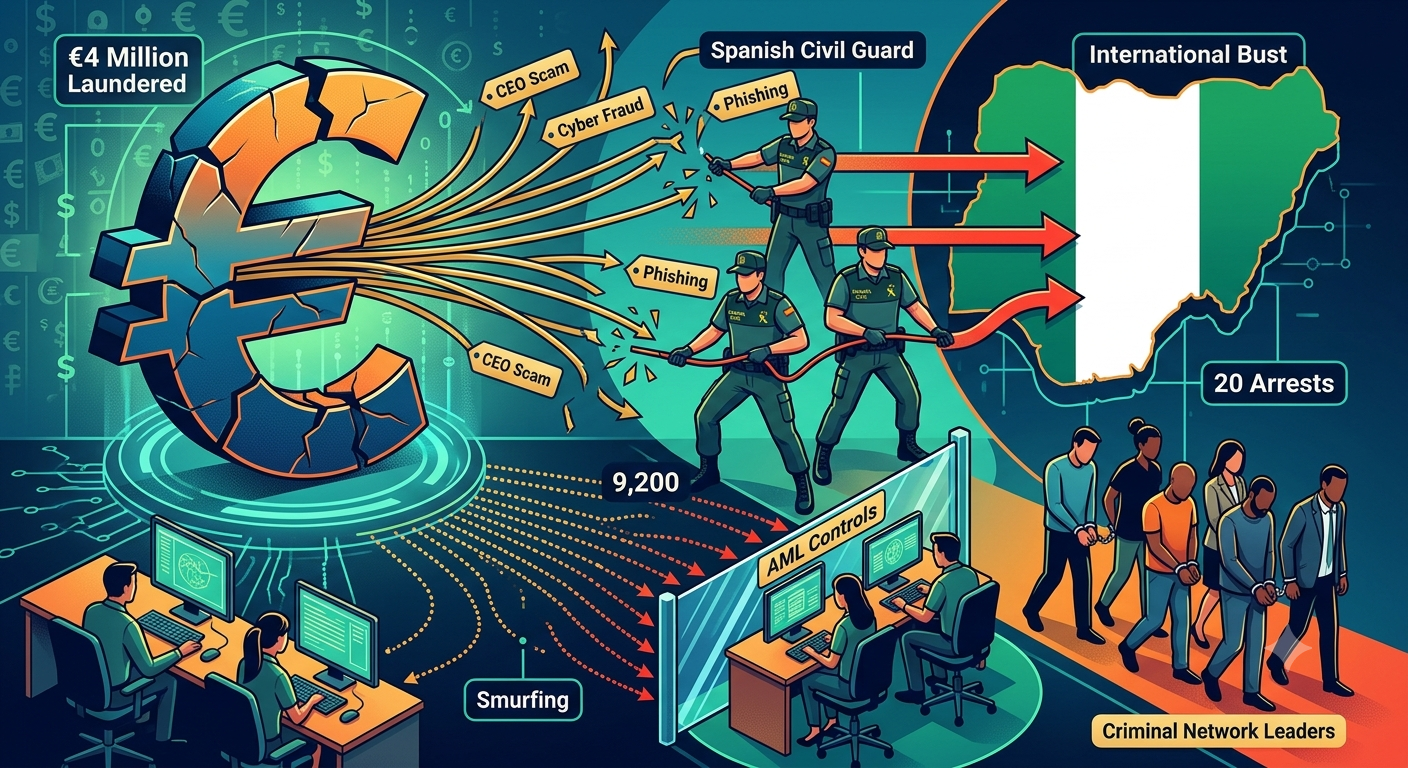
A network that laundered more than four million euros from scams by sending the money to Nigeria falls
Spanish Police Bust €4 Million International Money Laundering Ring Bound for Nigeria. The Spanish Civil Guard has dismantled a criminal network responsible for laundering over €4 million generated through cyber fraud, CEO scams, and identity theft across Europe. The organization utilized "smurfing"—splitting large illicit funds into more than 9,200 small-wire transfers using falsified passports and stolen identities—to bypass anti-money laundering controls and funnel cash into Nigeria. The two-phase operation led to 20 arrests, investigations into 11 others, and raids targeting key leaders in Bilbao as well as several complicit money transfer agencies.
No recommended articles found.